

B2B identity management
Give every organization its own branding, federation, delegated administration, and data residency. All in one product that your team configures and your partners can manage themselves.
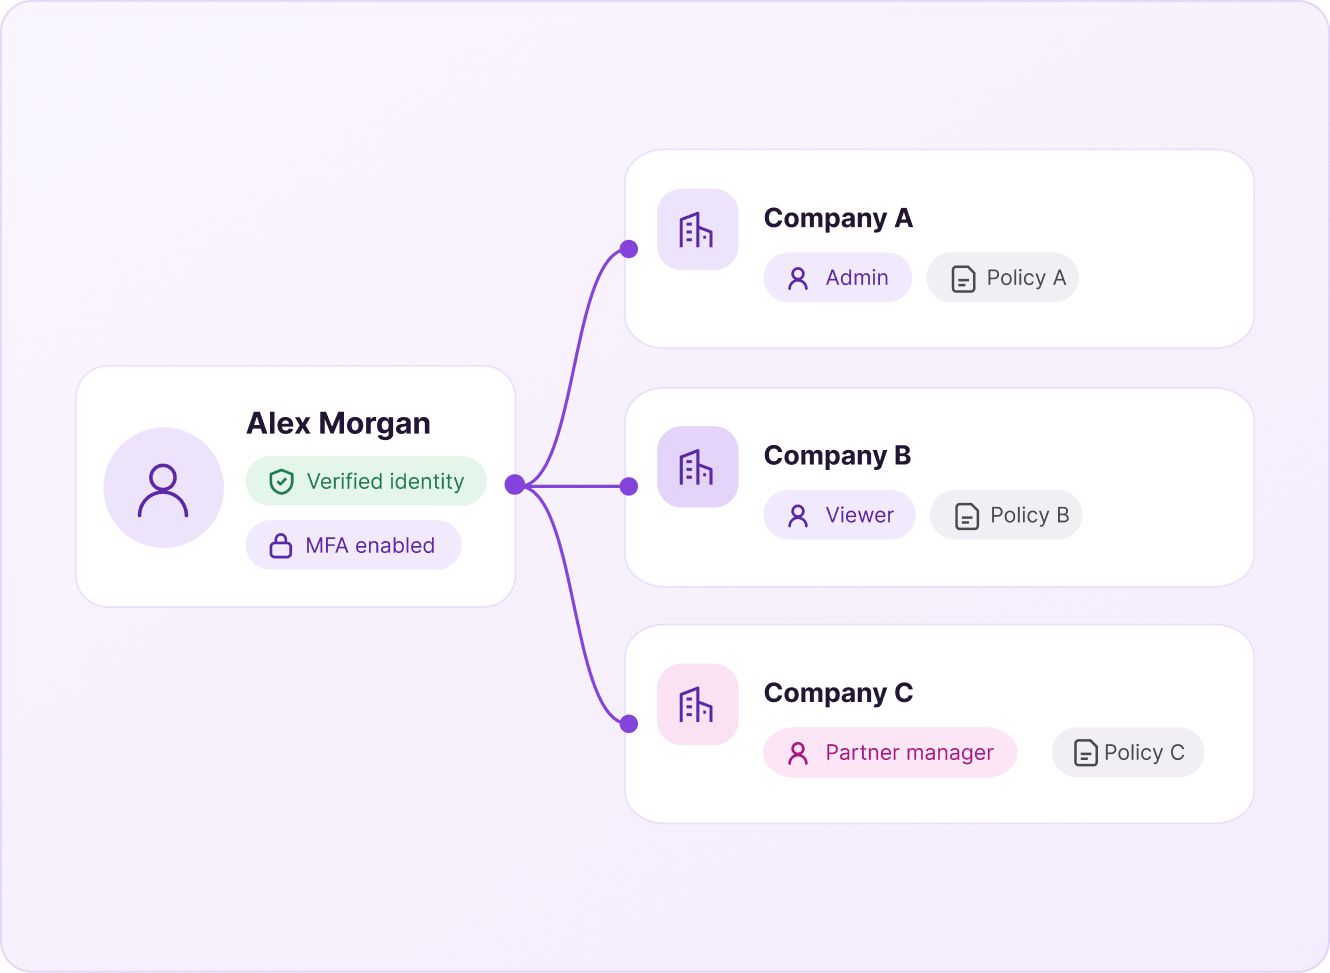
Support B2B, B2B2C, and hybrid models
Signs your B2B identity needs an upgrade


One product for B2B, B2B2C, and hybrid identity
Each organization can have its own branded sign in experience, identity provider configuration, policies, and account management experience.
How Strivacity handles B2B differently
Our differences are in depth, defaults, and what you get on day one versus what you have to build yourself.
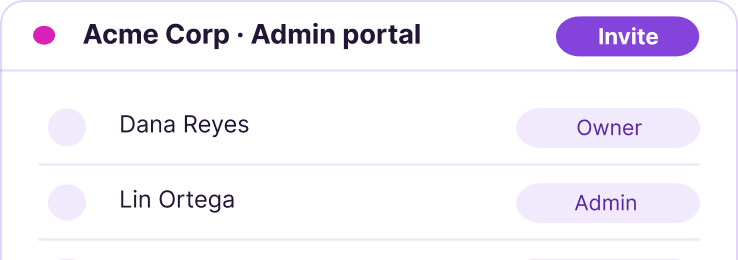
Give customers an admin portal on day one
Strivacity gives your B2B customers a ready-to-use administration portal where they can manage accounts, invite and remove users, update roles, and grant or revoke what AI agents can do for their users.

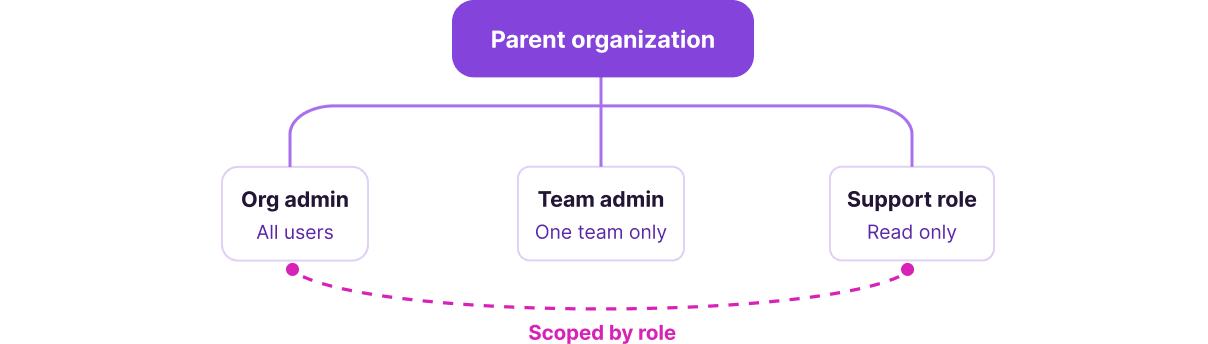
Full-depth delegated administration
Cross-organization grants let one administrator manage users and their AI agents across an entire hierarchy, from a parent organization down to individual teams. Granular RBAC controls come out of the box, so your most complex setups are covered.
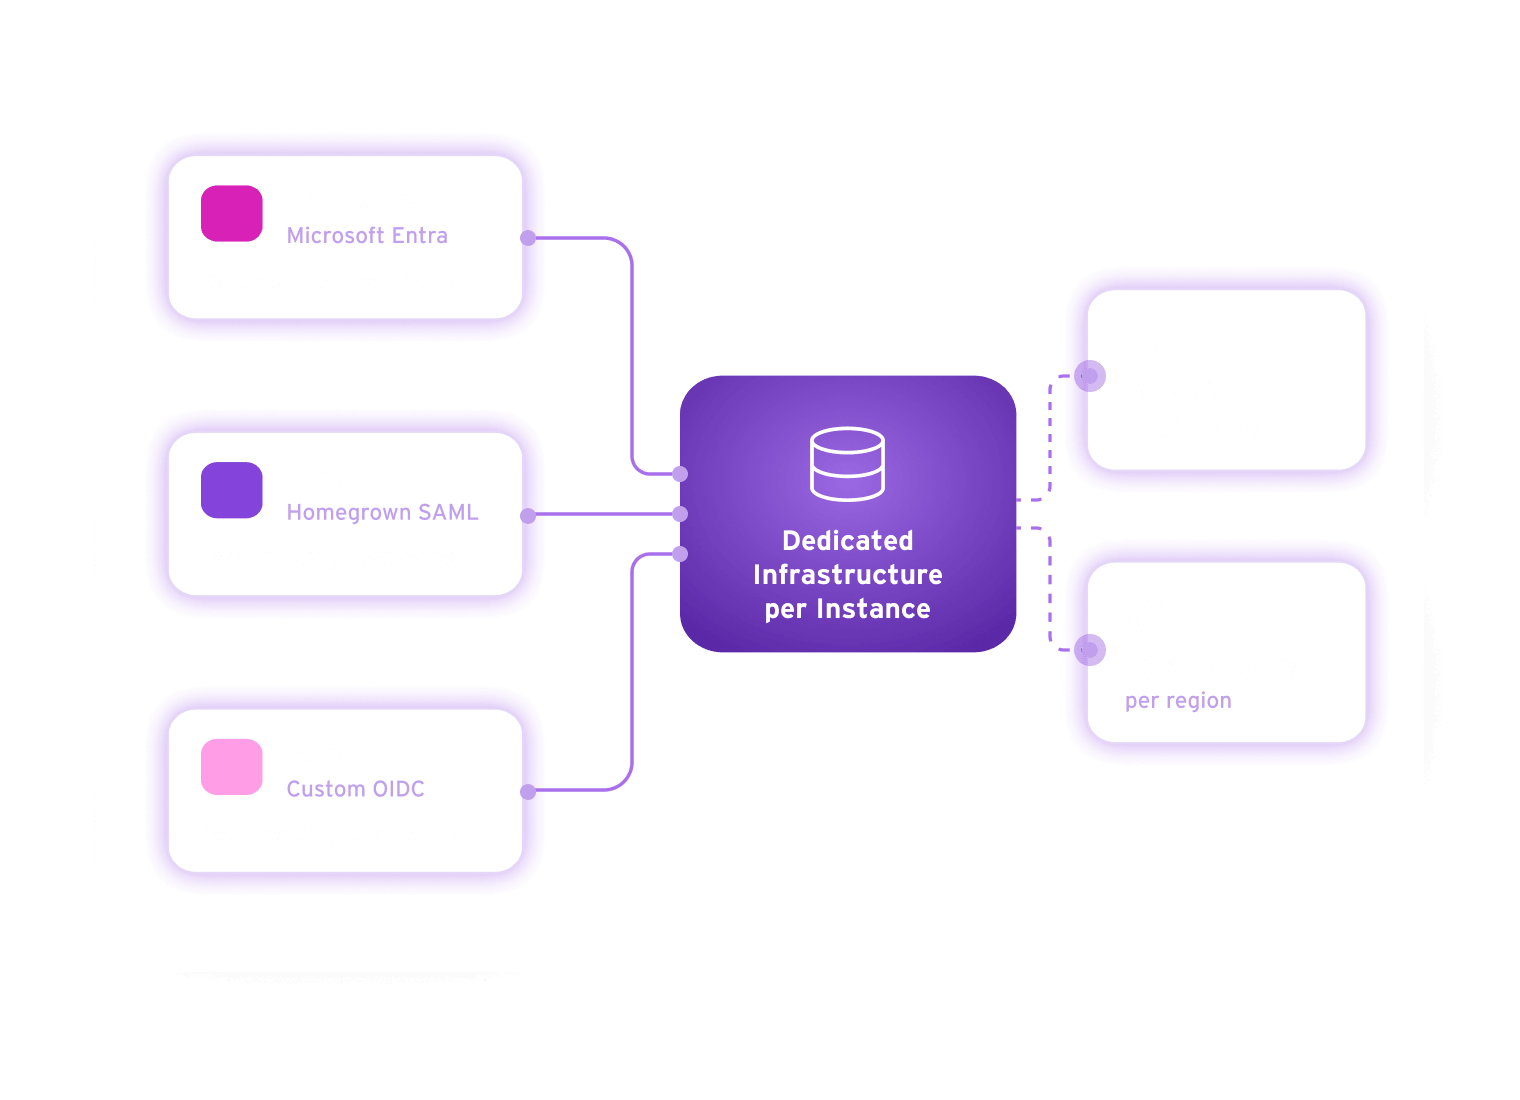
Dedicated infrastructure, by default
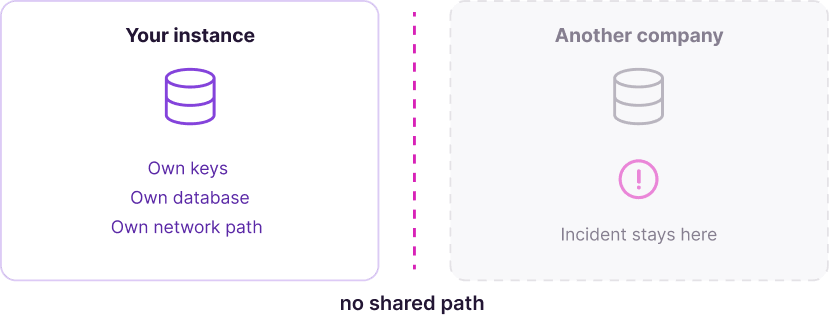
Every Strivacity customer gets a fully isolated environment: dedicated infrastructure, no shared keys, databases, or network paths. That isolation absorbs bursty traffic and lets you set policies, branding, and audit reporting for each partner.
Data residency built into the architecture
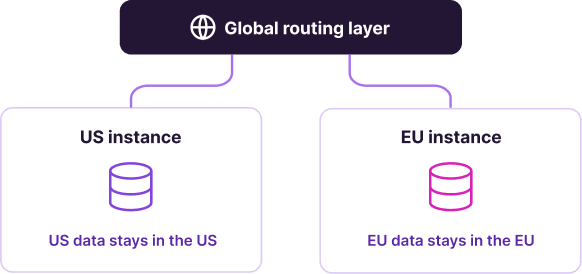
When your B2B partner is in a different jurisdiction, Strivacity can run a separate, isolated instance per region, so their users’ and agents’ data stays in region. E.g. a US brand with a European partner runs two instances.
Let every partner bring the IdP they already use
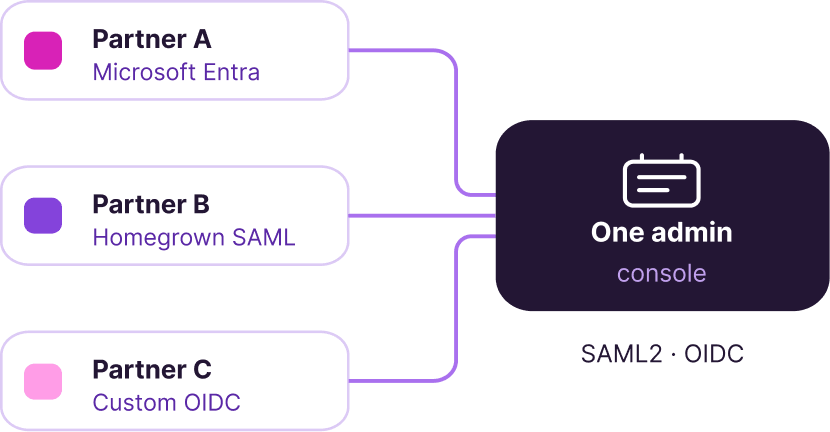
Each organization brings its own identity provider, independent of every other organization in the same instance. Strivacity connects to all of them using SAML 2.0 and OpenID Connect, the standard protocols for enterprise sign-in. You manage every connection from one admin console, with per-organization overrides for branding, access policies, and authentication flows.
Partners that haven’t migrated off a legacy or on-premises IdP can federate today. No forced migration, no precondition for onboarding.
Strivacity vs. other B2B identity vendors
In B2B customer identity, architecture decides what you get out of the box and what your team has to build.
Strivacity
Typical approach in the market
Organization account and user management portal
Pre-built portal, ready on day one. B2B customers manage their own accounts, roles, and users. No developer work required.
Some vendors embed an admin portal within your application, requiring integration into your product. Others provide API toolkits and components that require building the admin UI separately.
Single-instance isolation
Every customer gets dedicated infrastructure. No shared keys, databases, or network paths. This is the default.
Isolated environments are usually a premium option. The default is shared infrastructure.
Cross-border data residency
A separate isolated instance per region, connected by a global routing layer. Each jurisdiction’s data stays in physically dedicated infrastructure.
Data residency is typically a logical control within shared cloud infrastructure, not physically separate infrastructure per region.
Scalability
Unlimited organizations per instance, with multi-level hierarchies supporting complex B2B2C structures including dealer networks, franchisee models, and multi-level delegation. Identity store scales to billions of identities.
Hierarchy depth and scale vary. Some products use flat lists requiring app-level workarounds, while others offer nesting with limits on depth, org count, or pricing tiers.
Agentic B2B
Humans and AI agents managed in one product, with scoped, revocable authority and a unified audit trail.
AI agents are typically handled by a separate product, built mainly for workforce use cases.
Why Strivacity for B2B identity?


Frequently asked questions
B2B CIAM, or B2B customer identity and access management, is the software layer that manages how your business customers and partners open accounts, sign in, and access your digital services. Also called B2B IAM or B2B identity management, it adds organizational hierarchy, delegated administration, federated SSO, and per-organization branding on top of the authentication foundation most CIAM products provide. Strivacity is purpose-built for B2B CIAM, supporting every major B2B model in a single instance, with dedicated infrastructure per customer and no forced migration from existing identity providers. CIAM differs from workforce IAM, which governs employee and contractor access to internal systems rather than customer access to your applications.
B2C identity optimizes for individual consumers, with low friction, self-service, and high scale. B2B identity adds organizational structure: multiple users under one business customer, role-based access within that organization, SSO federation to the customer's own identity provider, and delegated administration so your customer manages their own users without involving your team. Strivacity handles both in a single instance, so organizations with both B2B and B2C customers don't need separate products or environments.
B2B2C CIAM manages identity for organizations that serve end customers through third-party partners, brands, subsidiaries, agents, or branches. A manufacturer selling through a dealer network, or a health insurance provider managing customers and patients through regional partners and hospitals, are both B2B2C models. Each partner needs its own branded experience, delegated administration, and customer data, while the parent organization maintains visibility and control over the entire structure. Strivacity supports B2B2C natively with multi-level organization hierarchies, per-organization branding, and cross-organization grants that enable partners to manage their own customers, all from one Admin Console.
Strivacity supports the major B2B identity models, including straight B2B, B2B2C, hybrid B2B and B2C, white-labeled dealer or partner arrangements, and multinational structures with country-specific account opening and data rules. All models run in a single instance without requiring separate environments for each.
Strivacity uses an organization structure to segment accounts within an identity store. Each organization supports delegated administration, organization-specific policies, per-organization branding, and independent IdP configuration. Administrators can manage a single organization or hold cross-organization grants to manage across a hierarchy, supporting multi-level structures for complex partner relationships without involving your team.
Yes. Delegated administration gives each organization's administrators a dedicated self-service portal to manage their own accounts, invite users, assign roles, and handle day-to-day access without opening a ticket with your team. Cross-organization grants let a single admin manage across a hierarchy, so even complex B2B2C structures can self-administer.
Federated identity management lets your B2B customers sign in using their own organization's identity provider, such as Microsoft Entra, Okta, or a homegrown SAML 2.0 setup, rather than creating new credentials with you. This matters for both security and user experience. Your customers sign in with the credentials they already have, with no new passwords or multi-factor authentication (MFA) methods to create, remember, or reset. Strivacity supports per-organization federation so each B2B customer brings their own identity provider independently, and partners still on a legacy or on-premises identity provider can federate today without migrating first.
Yes. Strivacity's localized deployment model runs a fully isolated instance per region, connected by a global routing layer that directs each customer to the right instance automatically. A US brand with a European partner can run two instances, one per jurisdiction, with each party's identity data staying in physically dedicated infrastructure in its region. This is not a logical separation within a shared cloud. It is the architecture.
Yes. Strivacity runs in financial services, insurance, and other regulated industries where data residency, audit isolation, and compliance reporting are requirements. Each customer's environment is fully isolated, so partner-specific compliance reports require no filtering across shared logs. Per-organization policy overrides support different compliance configurations across partner organizations in the same instance.
Yes. Each organization in Strivacity configures its own identity provider independently, whether that is a commercial provider like Microsoft Entra or Okta, a homegrown SAML 2.0 implementation, or a legacy on-premises identity provider. There is no forced migration. Partners federate through whatever they have today, and migrations can happen at their own pace and on their own terms.
Strivacity gives each agent a verifiable identity using the same standards as human sign-in, scopes what it can do on behalf of the person who delegated it, and lets customers grant or revoke that authority through self-service. Human and agent activity appears in one audit trail, so you can always tell who acted and whether it was authorized.
Give your B2B customers enterprise-grade identity
Secure, intelligent access management built to enable trusted digital interactions at scale.
