

Customer identity and access management (CIAM) migration.
Customer identity (CIAM) migration means moving your customer identity data and sign-in journeys from one identity solution to another without disrupting customers actively using your product.
With a careful approach and a vendor that provides documented tooling and support, you can manage this risk. This page covers why organizations migrate, what the process involves, the three migration approaches, and what to look for in a replacement.
Why organizations migrate their CIAM


How Strivacity supports CIAM migration
Strivacity is built for organizations ready to move on from legacy CIAM, whether that means Okta, Ping Identity, ForgeRock or a homegrown system. Pre-built migration plug-ins, configurable journeys, APIs and extensibility help take the heavy lifting out of migration, without forcing you into a one-size-fits-all approach.
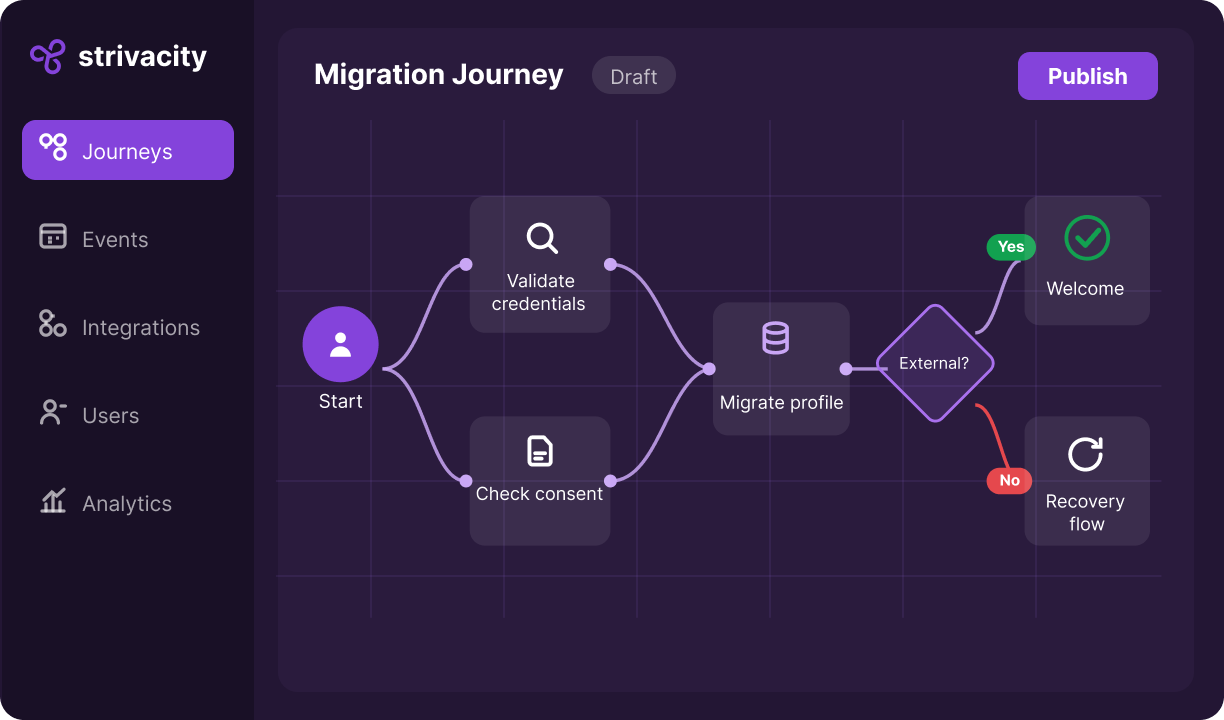
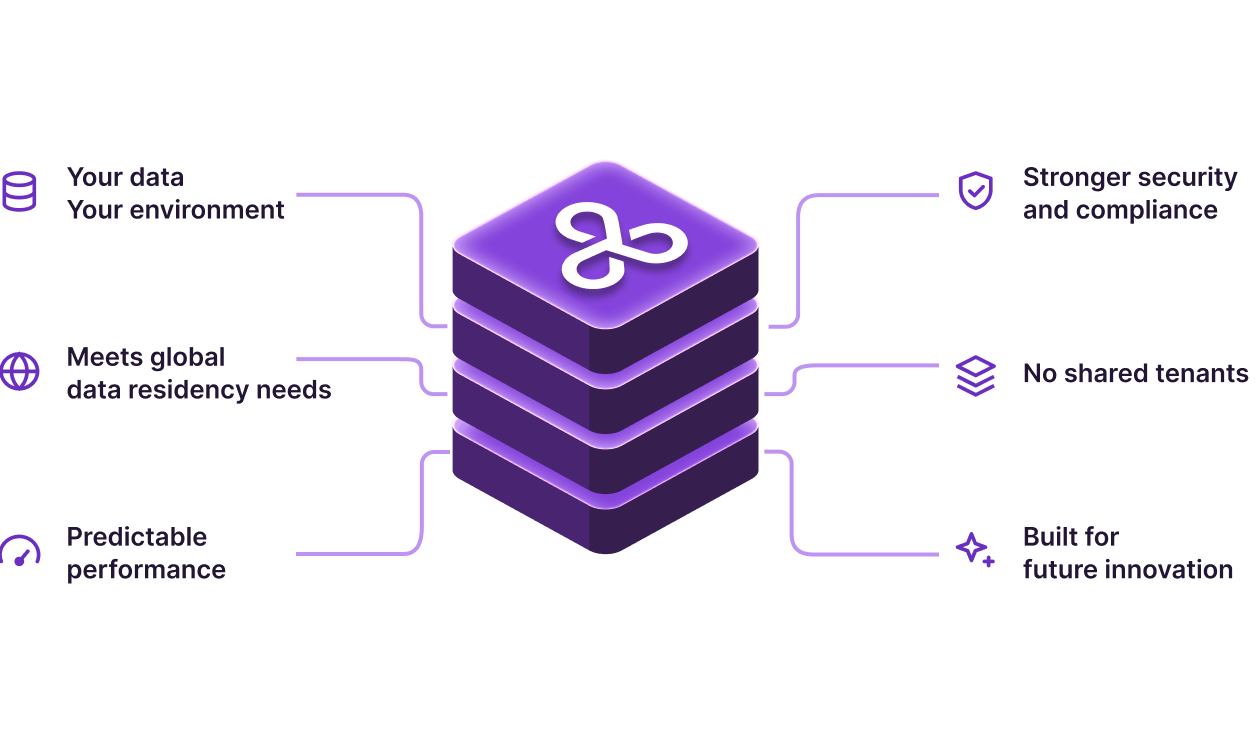
More importantly, migration shouldn't become your customers' problem. Strivacity gives you the flexibility to move identities and credentials with minimal disruption while modernizing the experience at the same time. And with a dedicated single-instance SaaS architecture, you can leave behind the performance, isolation and data residency constraints that often drive CIAM migrations in the first place.
Organizations that have migrated with Strivacity report real results.
- A CISO at a top-ranked university retired roughly 80% of custom code after replacing Ping Identity with Strivacity, and showed proven cost savings and improved customer conversion.
- A CISO at a top-20 US bank cited about $2M in savings compared to prior Okta and Ping Identity spend.
- Mohegan's migration went live within weeks, at lower cost, without adding headcount to manage it.
Migration approaches
The right migration strategy for your organization depends mainly on whether you can access password hashes from the legacy system, the size of your identity population, and how much customer disruption you can tolerate. Here's a quick comparison:
What it is
Best suited for
Bulk import with password hashes
A one-time, large-scale transfer. Identity data and password hashes are exported from the legacy system and imported in bulk. Customers sign in as usual with no reset.
Organizations with hash access that want a fast, clean, one-time cutover
Just-in-time (JIT) migration
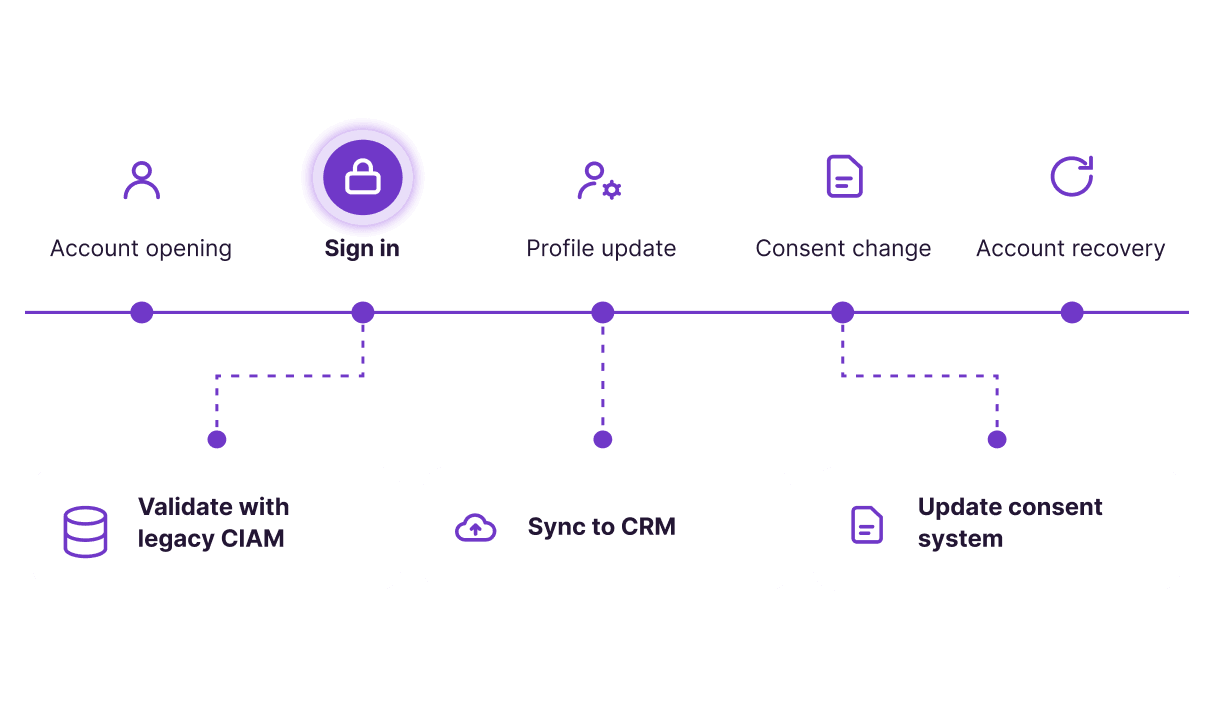
Identities move to the new system gradually, triggered by sign-in. Credentials are validated against the legacy system, then created in the new one, with no forced reset.
Large identity populations, or hash access is unavailable but a smooth customer experience is the priority
Bulk migration without password hashes
A one-time, large-scale transfer with no hash access. Customers reset their password on first sign-in after cutover.
Situations where everyone must move at once and hash access is not available
Sequencing the rollout
Any of the three approaches above, run in phases rather than one single event. Migrate audience by audience, application by application, or region by region.
Organizations that want to build migration experience before tackling harder segments, or need to meet regulatory requirements around the order of data residency changes
Not all CIAM providers give you access to password hashes. Where they do, check which hashing algorithms (the method used to scramble passwords for storage) are supported. Strivacity supports SHA256, Drupal-compatible SHA512, SHA1, MD5, Argon2, and BCrypt, among others.
This approach avoids forced password resets and lets you validate the new system at scale before full rollout, but it means running both systems in parallel for a while. As a general guide, plan to keep the legacy system active for at least 60 to 90 days while customers transition over, then decommission it once migration is mostly complete.
Done strategically, though, this can work in your favor. It's a clean slate for security improvements, it guarantees outdated or compromised credentials aren't carried forward, and it's a natural point to introduce passkeys or MFA. A well-communicated reset process can even re-engage customers who'd become inactive.
What CIAM migration involves
In a CIAM migration, you move identity data, rebuild or adapt sign-in journeys, reconnect integrations, and manage the transition for people actively using your product. All without breaking their experience.
The core components of a migration are:
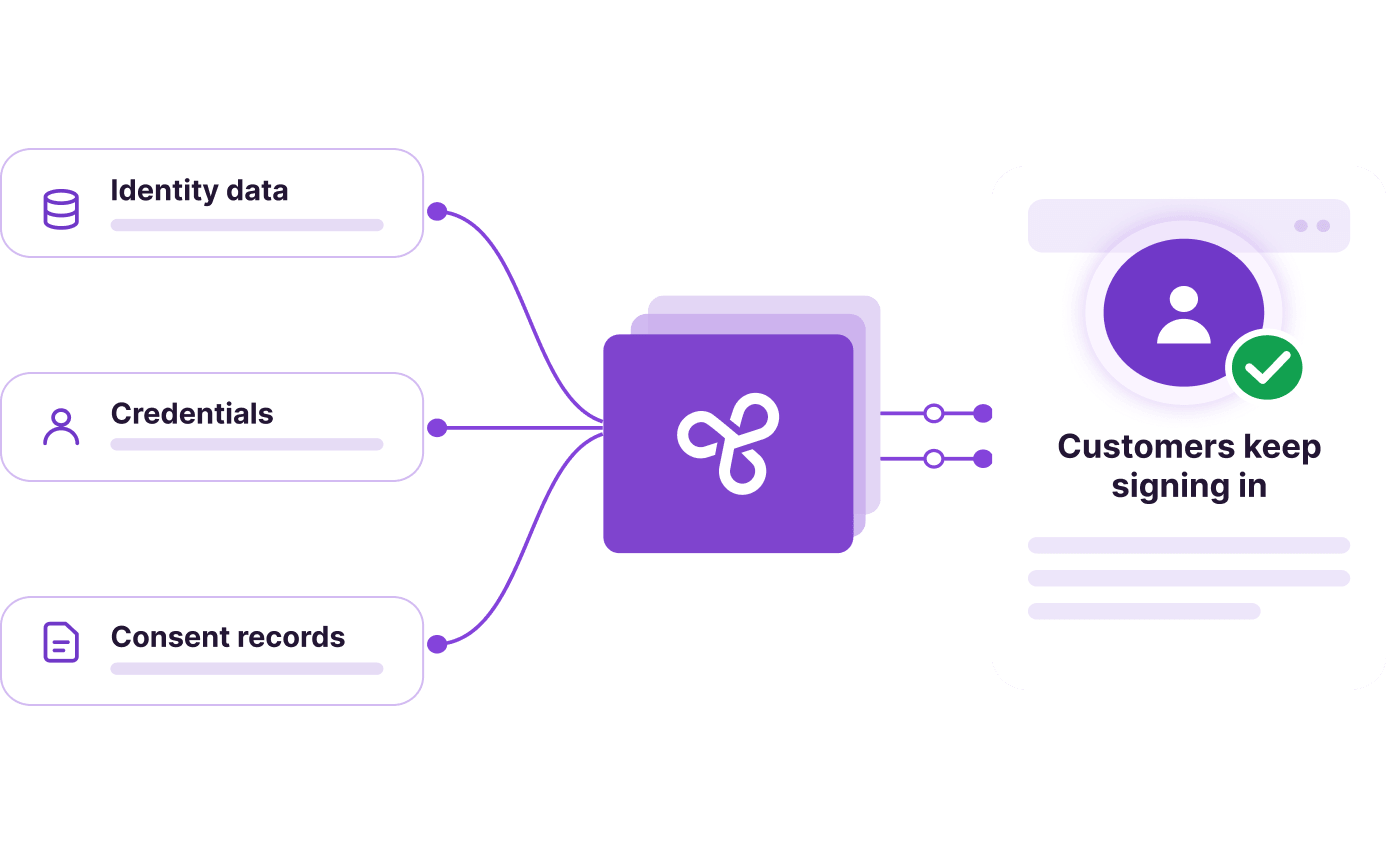
Identity data export and mapping
Pull customer identity records out of the legacy system and map them to the new system's schema. This includes credentials, profile data, consent records, and MFA (multi-factor authentication) enrollments.
Credential handling
Password migration should avoid plaintext credentials, so the preferred approach depends on whether you have access to password hashes from the legacy system.
Journey reconstruction
Rebuild or adapt account opening, sign-in, account recovery, and self-service flows in the new system. Use this as a chance to modernize and simplify these flows rather than copying the old behavior exactly.
Integration reconnection
Reconnect every downstream system connected to the legacy CIAM, like your CRM, analytics, fraud tools, and data warehouses, to the new solution.
Session management
Handle active user sessions gracefully during cutover so customers aren't unexpectedly signed out.
Cutover and validation
Make the final switch from legacy to new system, then validate that all flows, integrations, and data are working as expected.
Common CIAM migration pitfalls
The organizations that run into the most trouble usually underestimate one of these:
What to do instead
Data quality in the legacy system
Audit the legacy identity store before migration begins. Duplicate records, orphaned accounts, and inconsistent schema will compound during migration if not addressed first.
Underestimating integration work
Map every system connected to the legacy CIAM before selecting a replacement. Reconnection timelines are frequently the longest part of the project.
Ignoring consent records
Preserve and migrate customer consent alongside identity data. Skipping this creates regulatory exposure, particularly under GDPR and CCPA.
No rollback plan
Define your rollback trigger and procedure before cutover begins. A tested rollback path significantly lowers the risk of committing to a cutover.
Replicating legacy flows exactly
Migration is a chance to modernize. Rebuilding legacy flows without questioning whether they still serve customers well misses one of the main benefits of switching.
What to look for in a CIAM replacement
The migration process itself is a major factor in vendor selection, and organizations that overlook this often find the switch harder than it needed to be.

Migration tooling and documentation
Look for documented migration guides, tested export and import tooling, and real experience moving customers off major incumbents. Ask how they handle credential migration and what support they provide during cutover.
Architecture fit for your requirements
If shared infrastructure, performance limits or data residency are driving your migration, choose a replacement built to solve them. A dedicated single-instance architecture keeps your data isolated for predictable performance and residency control.
Integration support
Check for pre-built integrations with the systems you need to reconnect, and how easy custom integrations are to build. A rich plug-in library and open APIs will significantly cut down reconnection work.
Long-term commercial model
Evaluate pricing against your projected growth, since models that charge per application or penalize volume get expensive as you scale. Look for unlimited application support and predictable pricing based on monthly active users (MAUs).
Analyst validation
Third-party recognition from analysts like Forrester offers independent validation of a vendor's capabilities and market standing. It can also help you make the case and build internal consensus around your final vendor choice.
Capability snapshot
Buying committees increasingly compare vendors on specific, named capabilities rather than broad category claims. Include the teams who will feel the impact most: product, engineering, customer experience, and marketing.
What to check
Protocol support
OAuth 2.0 and OpenID Connect support, plus SAML compatibility for legacy integrations
MFA and passwordless
Native support for passkeys, FIDO2 biometrics, magic links, and soft tokens
Fraud prevention
Bot detection, credential stuffing prevention, breached password detection, and whether it is included or transaction-priced
AI agent identity support
Whether the solution is built to also authenticate and govern AI agents acting on a customer's behalf
Data residency
Single-instance versus shared multi-tenant architecture, and where the instance is hosted
B2B and partner identity support
Can customer/partner organizations manage their own users with secure and simple delegated admin experiences
Configure or code customization
Can you configure standard flows without engineering involvement, with option to extend with custom logic
Compliance and consent management
Native support for versioned consent records, auditable receipts, and preference management centers

Frequently asked questions
Bulk import with password hashes, just-in-time (JIT) migration, and bulk migration without password hashes. The right one depends on your access to password hashes, your customer experience goals, and your security requirements.
It depends on scope. The credential migration step itself, if password hashes are accessible, typically takes days to weeks. A full migration project, including integration reconnection and journey rebuilding, more commonly takes three to nine months end to end. Organizations that invest in pre-migration data quality work and use a vendor with documented migration tooling tend to complete faster.
Yes. Migrations from Okta and Ping Identity to alternative CIAM solutions are well established. Both vendors export identity data in standard formats, and experienced CIAM vendors have documented migration guides for both. The complexity depends primarily on the number of applications and integrations connected to the legacy system.
If password hashes are accessible, they can be carried over directly, and customers sign in as usual with no reset. If hashes aren't accessible, JIT migration validates and re-hashes credentials as customers sign in, also without a forced reset. If everyone needs to move at once and hashes aren't available, customers reset their password on first sign-in after cutover.
For JIT migration, plan to keep the legacy system active for at least 60 to 90 days while customers transition over, then decommission it once migration is substantially complete.
Export consent records from the legacy system and import them into the new CIAM solution in a format that preserves the original consent timestamp, version, and scope. This is a regulatory requirement under GDPR and CCPA. Make sure the replacement vendor supports auditable consent record migration and can show you how historical consent is preserved.
CIAM modernization means moving from legacy or homegrown identity infrastructure to a modern cloud-native CIAM solution. It often accompanies a migration but also includes redesigning identity journeys, adopting passwordless authentication, implementing consent management, and building in the extensibility needed to support future use cases such as AI agent identity governance.
Ready to move beyond legacy CIAM?
Secure, intelligent access management built to enable trusted digital interactions at scale.
